News News Official
Nintendo Switch 2 jailbreak advances with ns2jb and CivSwitch, but a full hack remains unconfirmed
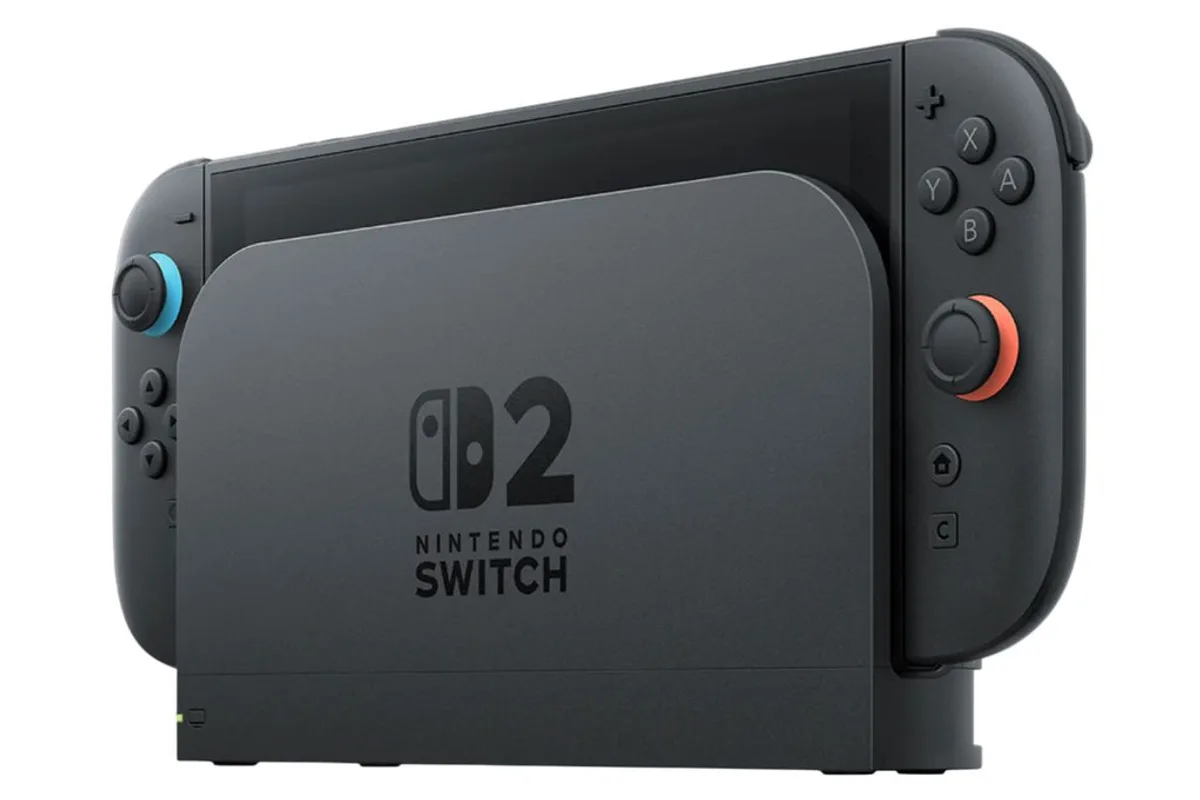
Nintendo Switch 2 security research has reached an important milestone. After ns2jb demonstrated unauthorized native code execution and modifications to Mario Kart World, another exploit using Civilization VII appeared on November 1, 2026. However, despite dramatic headlines, Nintendo's console has not been shown to be completely unlocked.
 By Maëlle
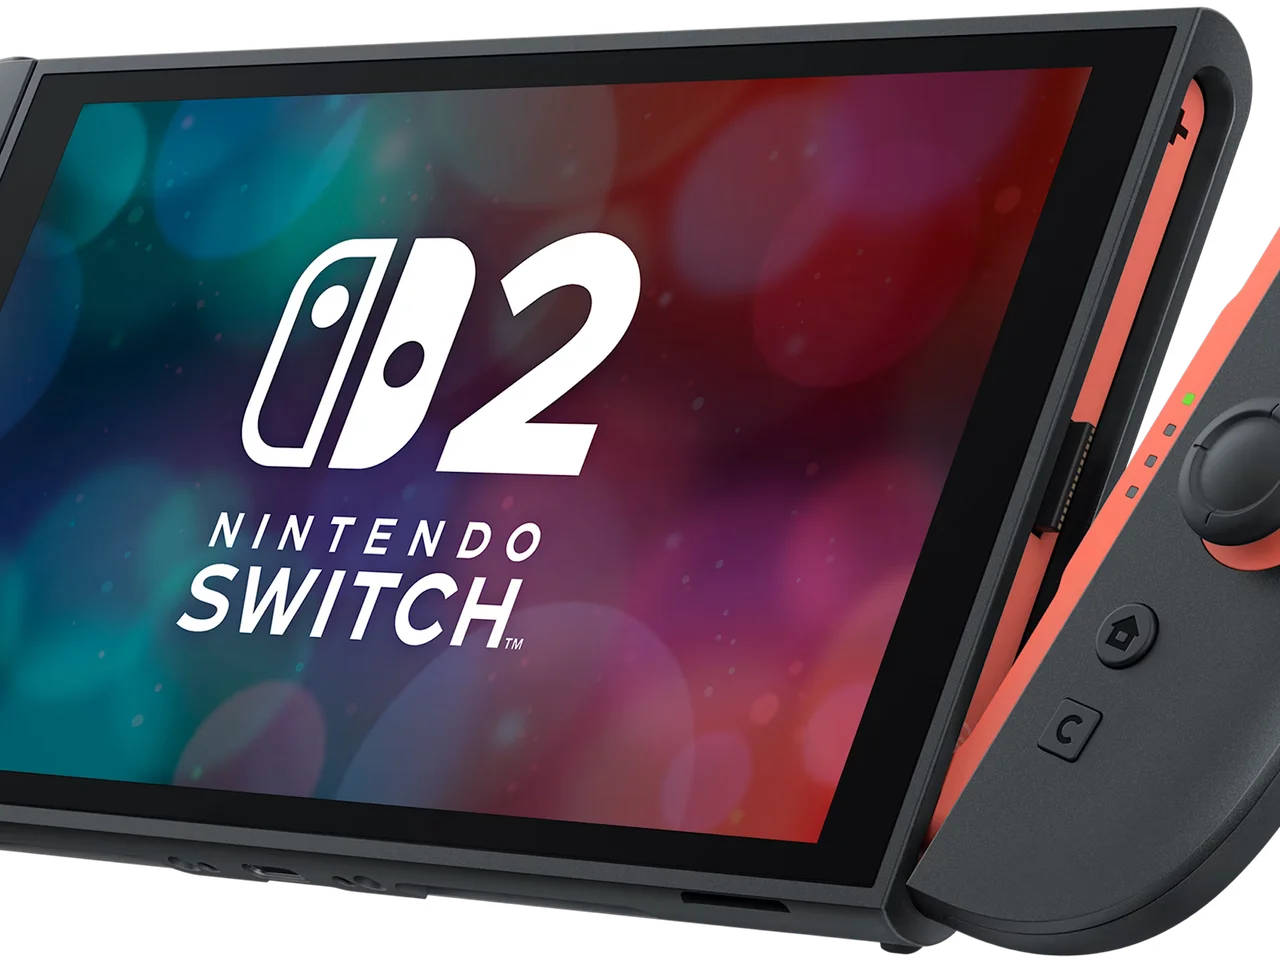
For more than a year, Nintendo Switch 2 resisted public attempts to achieve extensive unauthorized software access.
Early research demonstrated restricted capabilities without providing meaningful control over the console's operating environment.
That situation changed in October 2026 with the publication of ns2jb.
The exploit opened new opportunities for homebrew applications, game modification and research into the system's internal components.
On November 1, another entry point called CivSwitch appeared.
These developments are significant, but they do not establish that the Switch 2 has a complete jailbreak comparable to the solutions available for some original Nintendo Switch systems.
The first major software jailbreak
Security researcher Sammy Hajhamid, known online as pepsipu, presented ns2jb on October 22, 2026.
His exploit does not require installing a modchip or soldering additional components inside the console.
The demonstration works on system software version 23.0.1.
The initial entry point is SmileBASIC 4, a programming application originally released for the first Nintendo Switch.
Because the newer console supports compatible original Switch software, the application can also run on Switch 2.
A vulnerability in its interpreter allows certain memory operations that should not be possible.
The researcher then used another vulnerability affecting the FileSystem system module to gain additional privileges.
Together, these issues enable native code execution outside the ordinary restrictions of the original application.
This represents an important advance beyond earlier demonstrations confined to limited software functions.
Mario Kart World receives unofficial characters
To demonstrate ns2jb, pepsipu modified Mario Kart World.
A video shows several unofficial characters participating in races.
The lineup includes Hatsune Miku, Peter Griffin, Cinnamoroll and the red Angry Bird.
The demonstration establishes that certain game assets can be modified on Nintendo Switch 2.
However, changing content in an existing game is not equivalent to completely bypassing commercial game protections.
The footage does not demonstrate that the console can universally launch unauthorized copies of all commercial releases.
It is a technical proof of concept rather than a consumer-ready piracy solution.
The first homebrew tools emerge
The release of ns2jb quickly attracted attention from Nintendo's homebrew development community.
Independent developers began demonstrating applications designed around the console's newly accessible capabilities.
On October 23, videos reportedly showing homebrew launchers appeared online.
These alternative interfaces are intended to organize software developed outside Nintendo's official ecosystem.
Other demonstrations have explored file transfers, development utilities and graphics capabilities.
However, a working experimental application does not establish broad compatibility or long-term stability.
The Switch 2 homebrew scene remains in its early stages.
Why ns2jb is not a complete jailbreak
The crucial distinction involves the level of access obtained.
Ns2jb allows native code execution with privileges associated with selected system modules.
It does not provide confirmed full control over the console's kernel.
The kernel manages fundamental operating-system mechanisms, including processes and essential security boundaries.
Without complete access to that layer, significant restrictions remain.
The exploit is also temporary.
It is described as tethered.
When the console restarts, the modifications executed in memory disappear.
The exploit must be activated again.
No persistent public custom firmware equivalent to Atmosphère on the original Switch has been established through this research.
SmileBASIC disappears from Nintendo's eShop
Shortly after ns2jb was revealed, SmileBASIC 4 disappeared from several regional Nintendo eShop listings.
Multiple technology and gaming publications observed the removal.
Its disappearance makes the original entry point more difficult to obtain for users who did not already possess the application.
However, Nintendo has not published a detailed technical statement definitively linking the removal to the vulnerability.
The timing makes that explanation plausible without independently confirming it.
A future software update could also address the vulnerabilities involved.
This differs from hardware-level security flaws that required physical revisions to protect later versions of the original Nintendo Switch.
CivSwitch introduces another route on November 1
Homebrew researchers have continued investigating alternative entry points.
On November 1, 2026, developer Gezine published CivSwitch.
The project uses the original Nintendo Switch edition of Civilization VII.
According to its documentation, the entry point involves a cross-site scripting vulnerability in the game's multiplayer chat system.
The exploit allows JavaScript execution within an application context.
Testing has been reported on Nintendo Switch 2, including firmware version 23.0.1.
The developer also describes a method for retaining an application-level trigger in saved data.
However, that persistence must not be confused with installing permanent custom firmware.
Executing code through a saved-game trigger does not mean every operating-system security boundary has been removed.
CivSwitch provides another experimental entry point rather than proof of complete system control.
WebKit research offers another possibility
On October 31, a researcher using the name jamesmykil presented another potential entry point involving WebKit.
The browser technology is used by certain applications and integrated web interfaces.
The demonstration used Drift Legends 2 to reach a web environment.
The researcher reported limited data manipulation capabilities inside that environment.
However, the available demonstration does not establish kernel-level access.
No stable public full-jailbreak solution has been confirmed from the project.
It remains another experimental research path.
Can the console run every game for free?
No verified demonstration establishes a universal method for running unauthorized copies of every commercial Nintendo Switch 2 game.
The demonstrated capabilities primarily involve native code execution, technical research, selected homebrew applications and game asset modification.
These are meaningful developments for independent programmers and security researchers.
They do not automatically provide a commercial-game loader.
An exploit does not necessarily defeat the console's encryption, license checks or secure boot mechanisms.
It would therefore be misleading to describe Nintendo Switch 2 as completely open to unrestricted software execution.
What are the risks?
The currently documented tools are primarily intended for technically experienced users.
Incorrect use can cause crashes, data loss or unexpected behavior.
Unauthorized modifications can also create risks involving access to Nintendo's online services.
The precise level of risk depends on the exploit, console configuration and the manufacturer's policies.
Users should also be cautious about programs claiming to install complete custom firmware instantly.
Promises of universal one-click unlocking are not supported by the public research examined here.
Including the word jailbreak in a program's name is not evidence that it is reliable or safe.
A significant compromise, but not complete control
The discoveries made in October and early November 2026 mark an important stage in Nintendo Switch 2 security research.
Ns2jb demonstrates that unauthorized native code can execute without hardware modification.
Early homebrew applications and CivSwitch show that additional developers are now exploring different ways to access the console.
The progress is real, but so are the limitations.
No complete kernel compromise or permanent consumer-ready custom firmware has been confirmed.
As of November 2, 2026, describing the Switch 2 as fully hacked would therefore be inaccurate.
The next stage of research concerns additional entry points and higher levels of system privilege.
Whether those efforts eventually lead to a complete alternative software environment remains an open question.